

Security at pipeit
Send privately.
Receive deliberately.
Files should reach the right destination. Encryption, device identity and permissions work together.
Send directly
Sent directly: encrypted end to end.
The end-to-end path applies when you send a file directly or through a server route: encrypted before transmission, decrypted only at the authorized destination.
- A server can relay encrypted content or hold it briefly to deliver it, without being able to read the file contents.
- The relay keeps nothing on disk and discards the encrypted data once it is delivered.
- Contents and metadata: even with encrypted contents, pipeit needs connection and delivery data to route a transfer. The privacy notice lists the data actually processed.
- This applies to direct transfers, not to files you keep in pipeit Cloud.
Devices and people
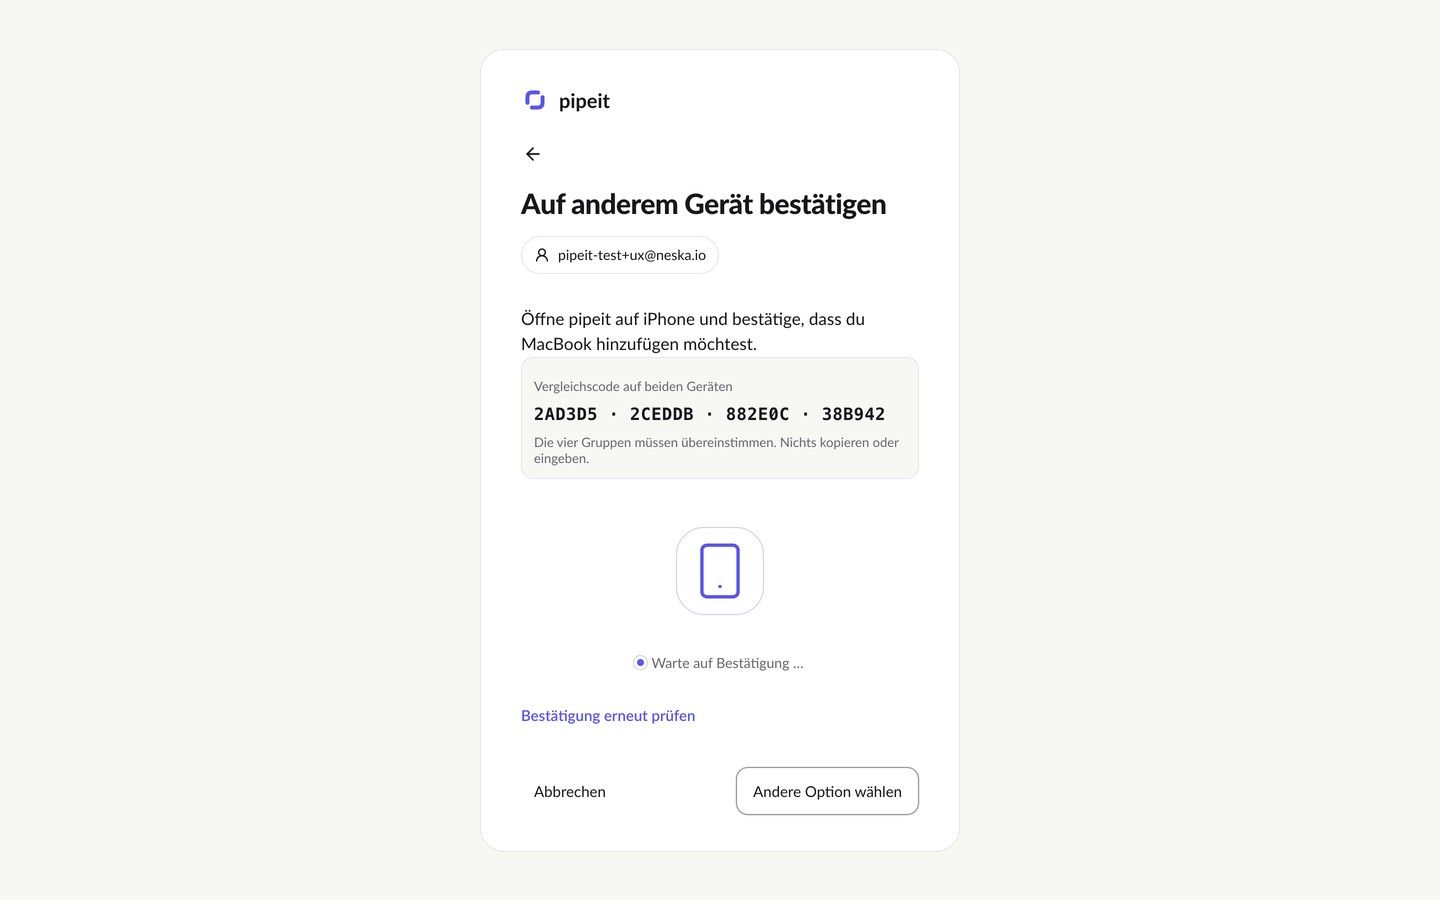
New device? You confirm it.
Devices and contacts have verifiable identities. A new device shows a comparison code, an existing one confirms it. Permissions determine who can send files to each destination.
- Comparison code on both devices: nothing to copy, nothing to type.
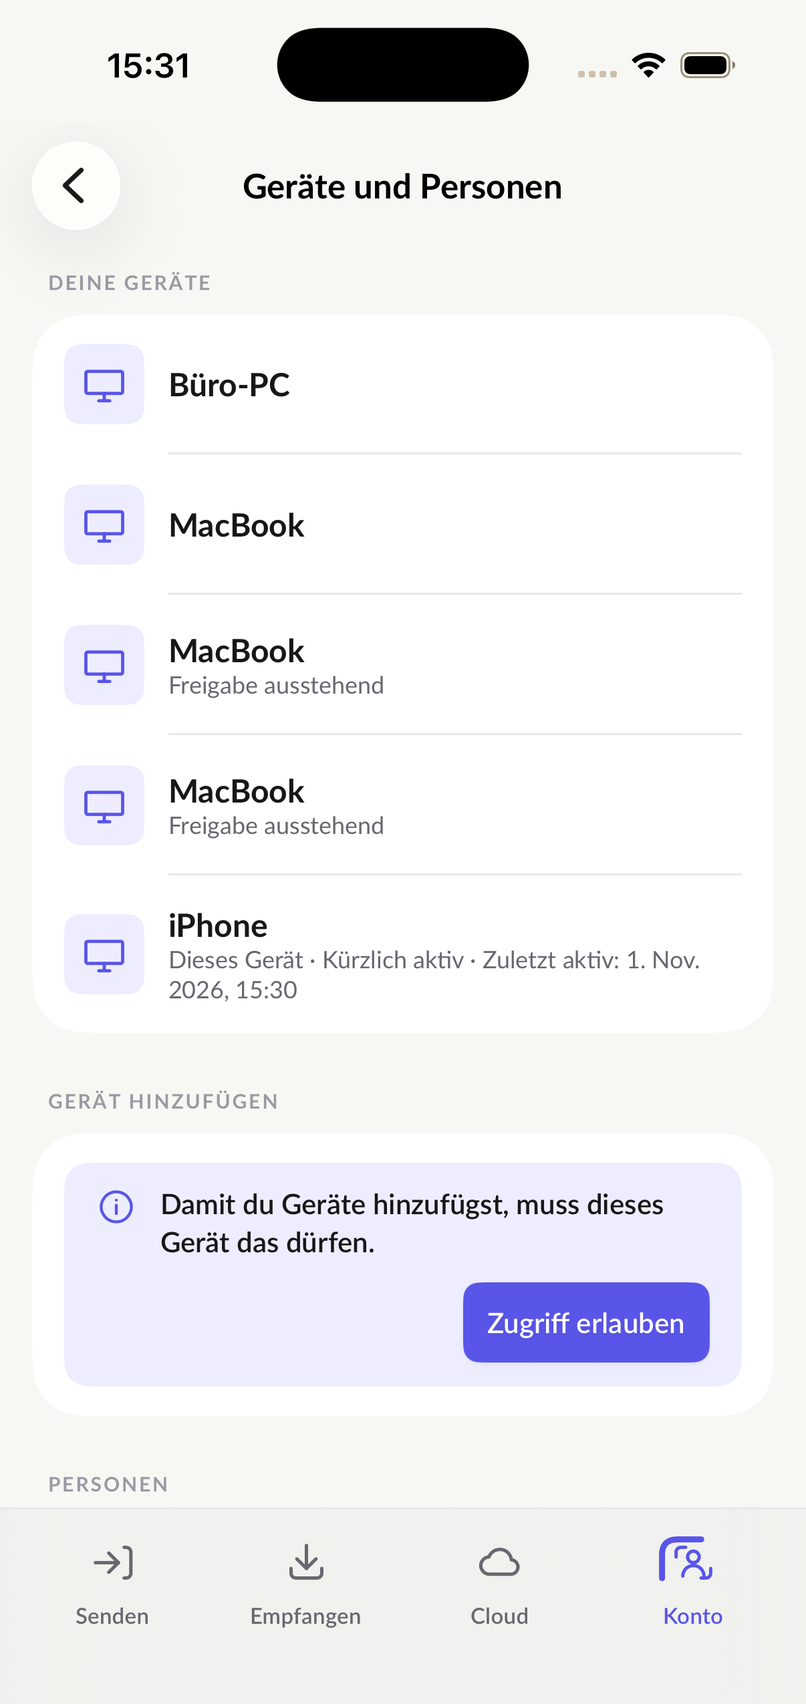
- Every device is named, checked and removed individually.
- Revoke access: devices and team access can be removed. This protects future access, but does not delete a file someone has already received.
Two ways, two promises
pipeit Cloud is different, on purpose.
Cloud files are stored so that the service can work with them: building search, creating thumbnails, scanning shared files for malware. That means the service can read them; they are not end-to-end encrypted. This does not change how direct transfers work.
- Send directly: private or sensitive files, servers, one-off hand-offs.
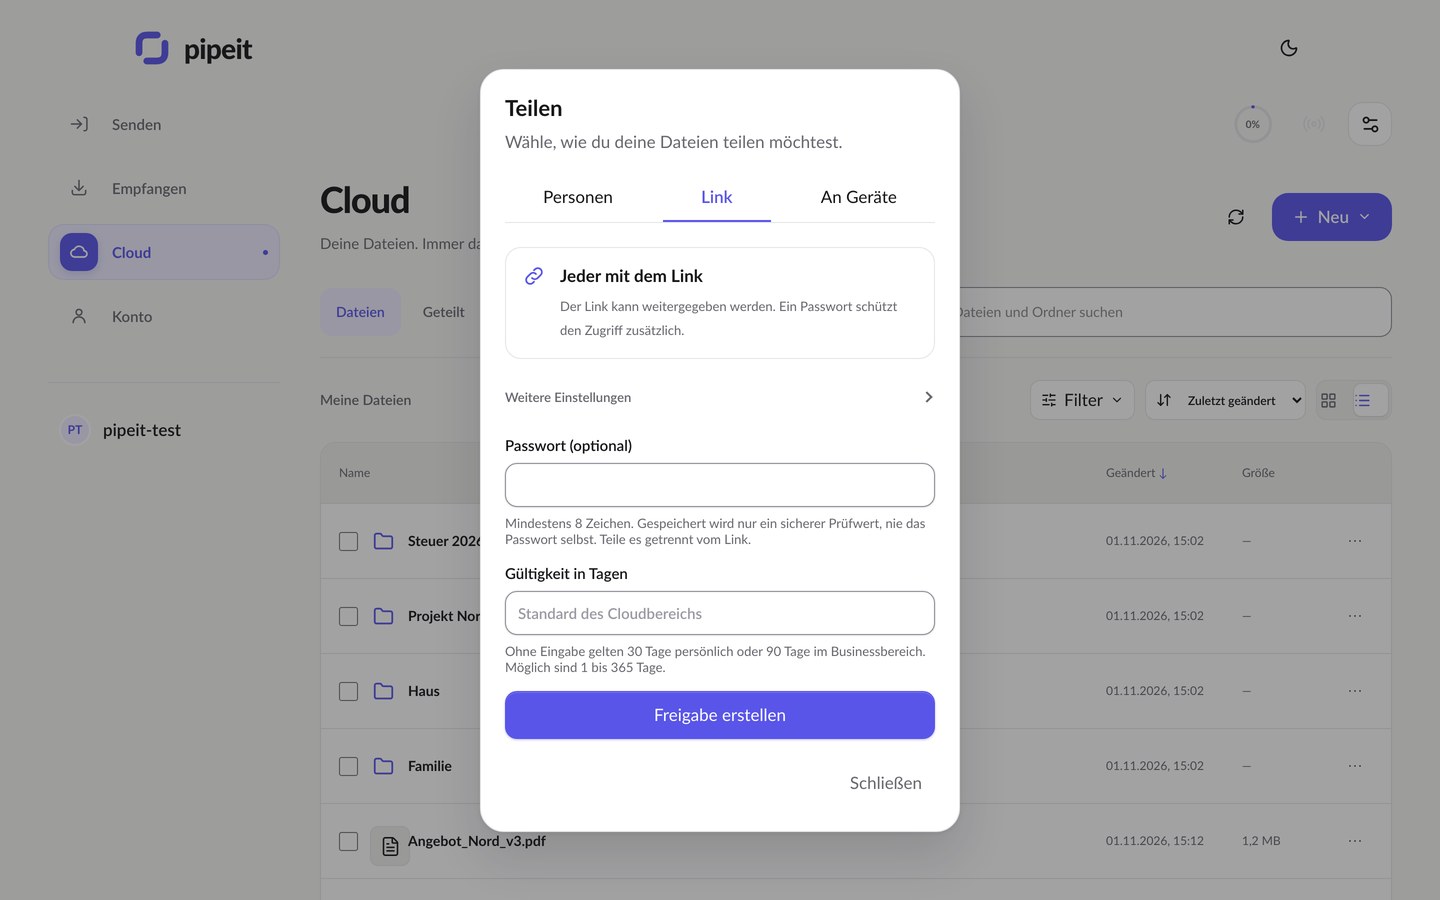
- Keep in the cloud: files you work with over time, share by link or want on several devices.
- Shared links with password, expiry date and a malware check before download.
AI workflows
From the AI chat: with a clear trust boundary.
A file created or uploaded in an AI chat is already known to that AI provider. To send it from there to a device end-to-end encrypted, a pipeit client you authorized on your computer performs the encryption. When the AI stores a file in your cloud, the cloud model applies.
Have a
security question?
Write to us via the contact page. For a security report, do not attach confidential files; we arrange a suitable channel first.
End to end on direct transfersDevices with comparison codeNo ads, no trackingOperated in Germany